Apple fixes critical flaw potentially tied to 'sophisticated' attack
On Sep. 28, Apple Inc. (Nasdaq: AAPL) released the security update iOS 26.7.1 and iPadOS 26.7.1. The update addresses CVE-2026-86950 through improved bounds checking. CVE-2026-86950 is an out
A
AnonymousCryptoCompass newsroom
September 29, 2026
2 min read
NEWS
CryptoCompass editorial visual for bitcoin coverage.
On Sep. 28, Apple Inc. (Nasdaq: AAPL) released the security update iOS 26.7.1 and iPadOS 26.7.1.
The update addresses CVE-2026-86950 through improved bounds checking. CVE-2026-86950 is an out-of-bounds write vulnerability that affects Apple's image rendering framework called CoreGraphics and allows arbitrary code execution when a device processes a maliciously crafted file.
An out-of-bounds write occurs when software writes data beyond an allocated memory area, creating conditions that attackers can potentially use to corrupt memory or run their own code.
Apple said it is "aware of a report that this issue may have been exploited in an extremely sophisticated attack against specific targeted individuals on versions of iOS before iOS 27."
The security update is available for iPhone 11 and later, iPad Pro 12.9-inch 3rd generation and later, iPad Pro 11-inch 1st generation and later, iPad Air 3rd generation and later, iPad 8th generation and later, and iPad mini 5th generation and later.
The blockchain security firm called SlowMist said Apple's latest security update is particularly relevant to cryptocurrency users because it has observed the iOS exploitation activity targeting sensitive wallet data.
However, the security firm did not attribute any crypto hacking incident to CVE-2026-86950.
SlowMist urged Apple users to install the latest security updates on their devices, and avoid installing apps from unknown or untrusted sources. It also advised users to not open suspicious links in Safari or in-app browsers, and treat unexpected files, links, and app installation prompts with caution.
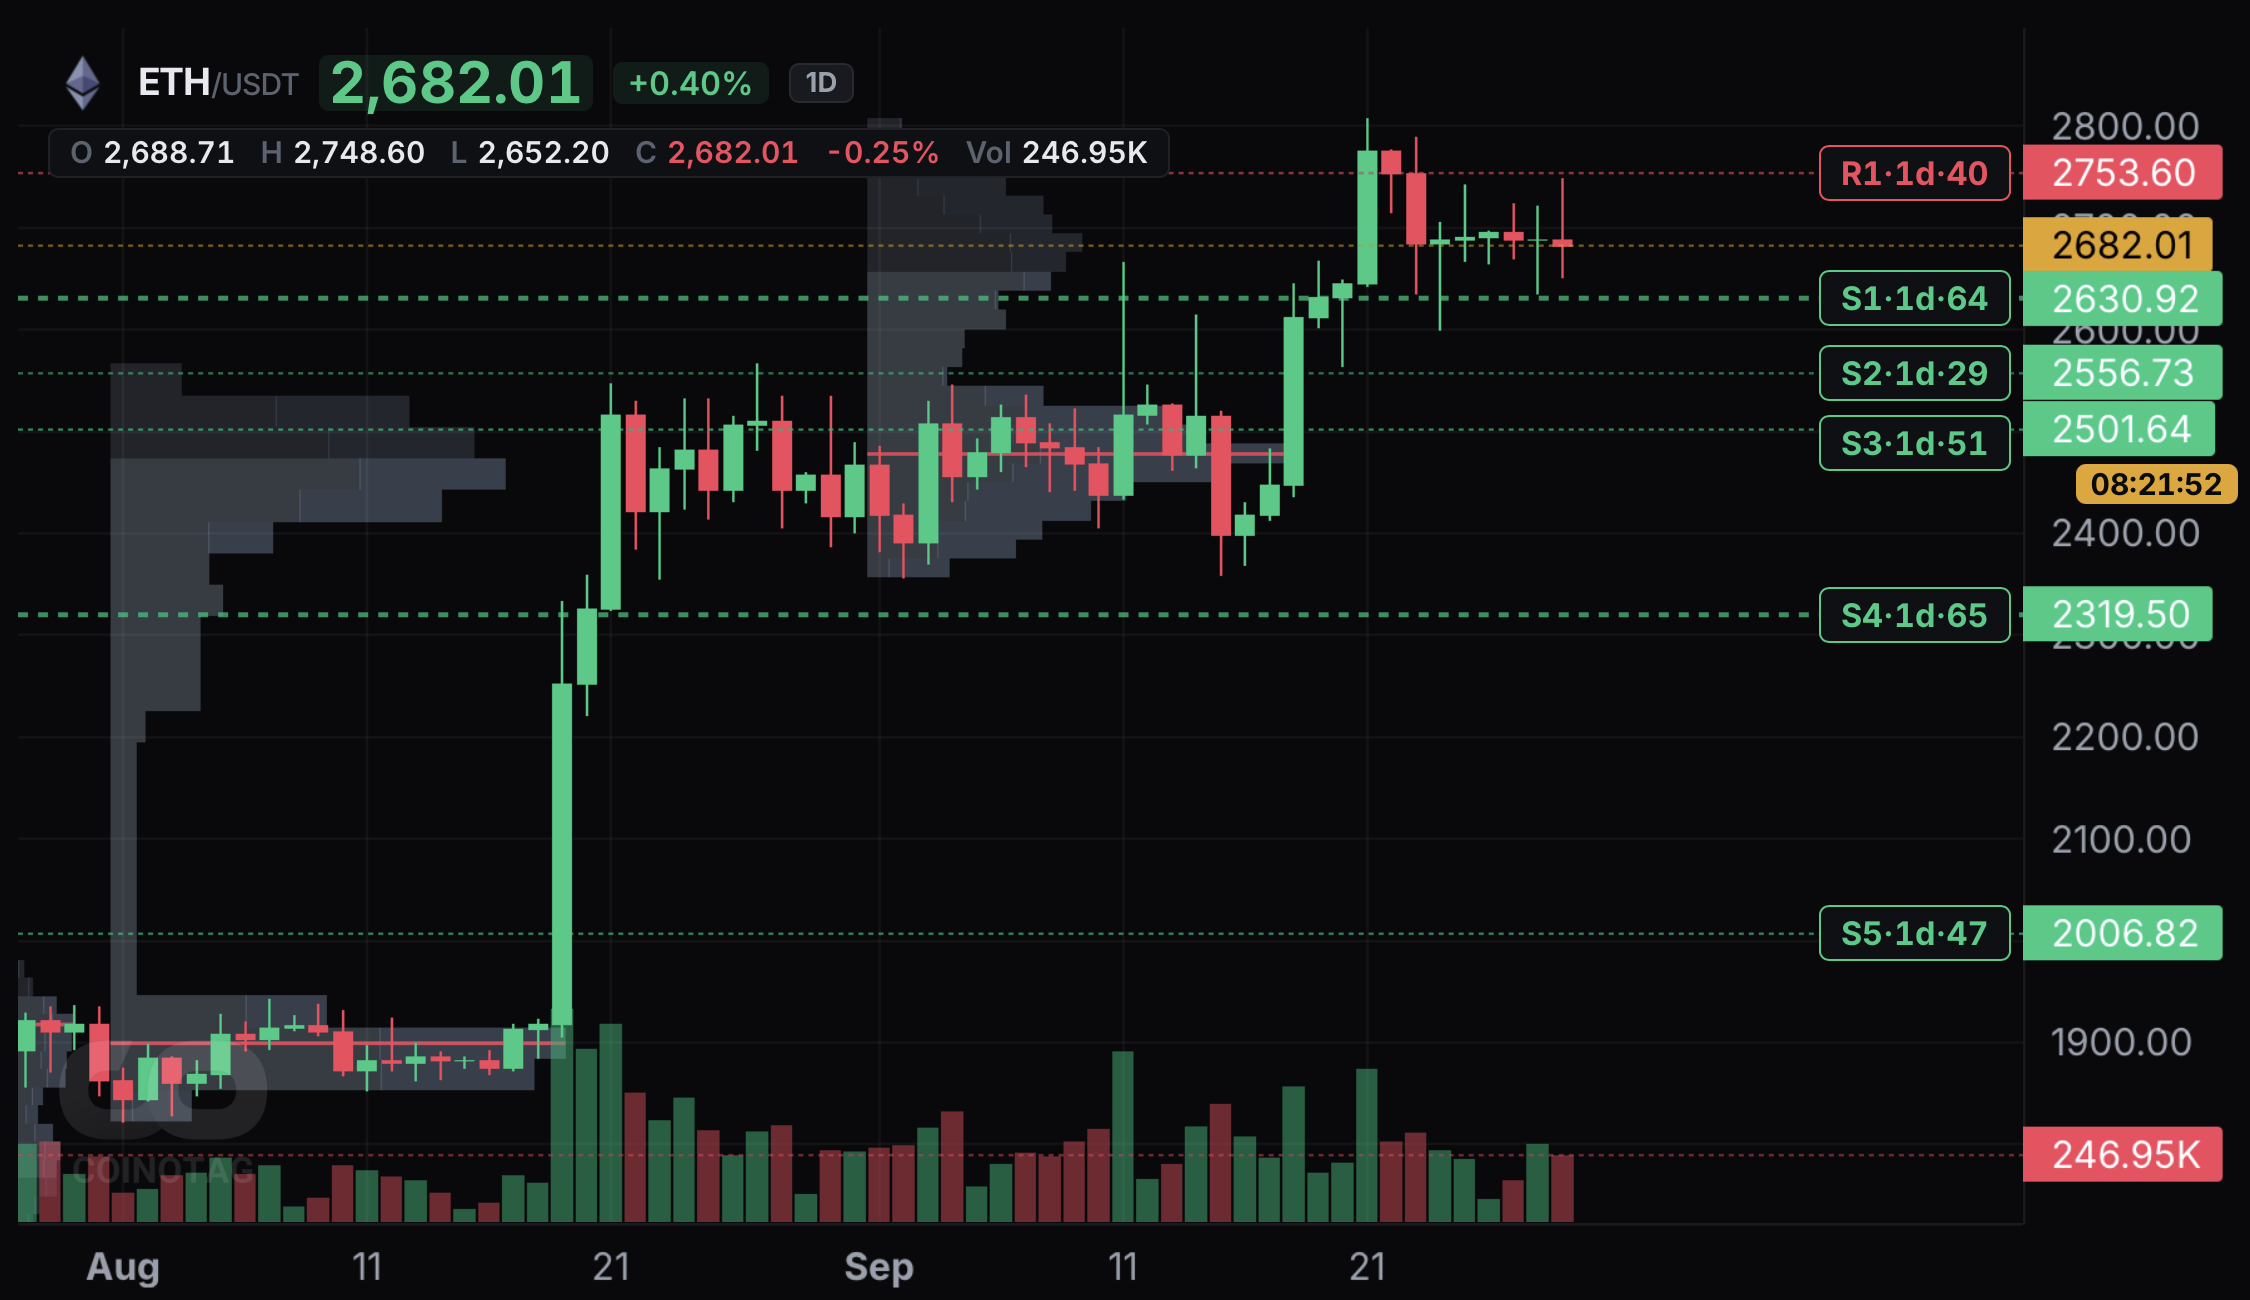
$270 Million Cleared in 24 Hours Leveraged long positions carried the loss in the crypto market over the past 24 hours, absorbing 64.05% of the $270.07 million in forced liquidations that swe
SEC staff added a no-central-party condition to guidance on buybacks involving functional non-security crypto assets. Buybacks for nonfunctional systems may raise investment contract issues w
HANetf has launched a euro-hedged Bitcoin exchange-traded product, giving European investors a route to Bitcoin exposure that incorporates a currency hedge against EUR/USD fluctuations. The p