Coinbase reported no evidence of unauthorized access to its own systems. Coinbase says a breach at third-party analytics provider Amplitude exposed contact information of a small subset of cu
- Coinbase reported no evidence of unauthorized access to its own systems.
- Coinbase says a breach at third-party analytics provider Amplitude exposed contact information of a small subset of customers.
- SlowMist’s 23pds claimed more than 70,000 users were affected, but Coinbase has not verified the figure. Customer funds remain unaffected, according to the exchange.
One of the largest crypto exchanges, Coinbase has denied claims that its systems suffered a data breach after a security incident at third-party analytics provider Amplitude exposed contact information belonging to a small number of its customers.
In a statement posted on its official support handle on X on October 28, the cryptocurrency exchange said the incident affected a small subset of Coinbase customer contact data, along with information associated with other companies using Amplitude.
Coinbase said it found “no evidence of unauthorized access” to its own systems and confirmed that customer funds were not affected. The exchange added that it was notifying impacted customers and regulatory agencies in line with its legal obligations.
The company has not disclosed the exact number of affected customers or provided a complete breakdown of the exposed information.
70,000 Coinbase Users Allegedly Affected, but Figure Remains Unverified
The clarification followed claims circulating online that hackers had obtained contact information belonging to more than 70,000 Coinbase users. The figure was attributed to a post by 23pds, the chief information security officer at blockchain security firm SlowMist.
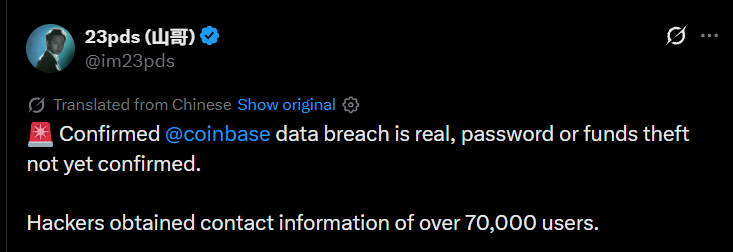 (Source: X)
However, Coinbase has not verified the reported figure, and the exchange’s statement describes the affected group only as a “small subset” of its customers.
Amplitude provides analytics services that help companies understand how people use their websites and applications. So, a security incident at an outside provider can expose customer information even when the company’s own systems remain secure.
The exposure of contact details can also create opportunities for phishing and impersonation scams, in which attackers pose as exchange employees to trick users into revealing account credentials or verification codes.
Coinbase has not reported any impact on customer funds. Also, there is no confirmed evidence that the incident gave attackers access to its internal systems.
The extent of the exposure remains unclear as the exchange continues notifying affected users and working with regulators. Further details, including the number of customers involved and the specific data exposed, have yet to be disclosed.