As of October 22, 2026, the CZ PHP warning is the biggest security story in crypto news today. Binance founder CZ told users on X to be careful before visiting any website in the coming days,
As of October 22, 2026, the CZ PHP warning is the biggest security story in crypto news today. Binance founder CZ told users on X to be careful before visiting any website in the coming days, after PHP patched two critical flaws on October 21, 2026.
Inhis post, CZ said some web admins are not always up to date with security patches, and he closed with “Stay SAFU!”
The CZ Binance warning raises one question: is it safe to visit crypto websites right now? CZ warns about websites in general, not one named platform.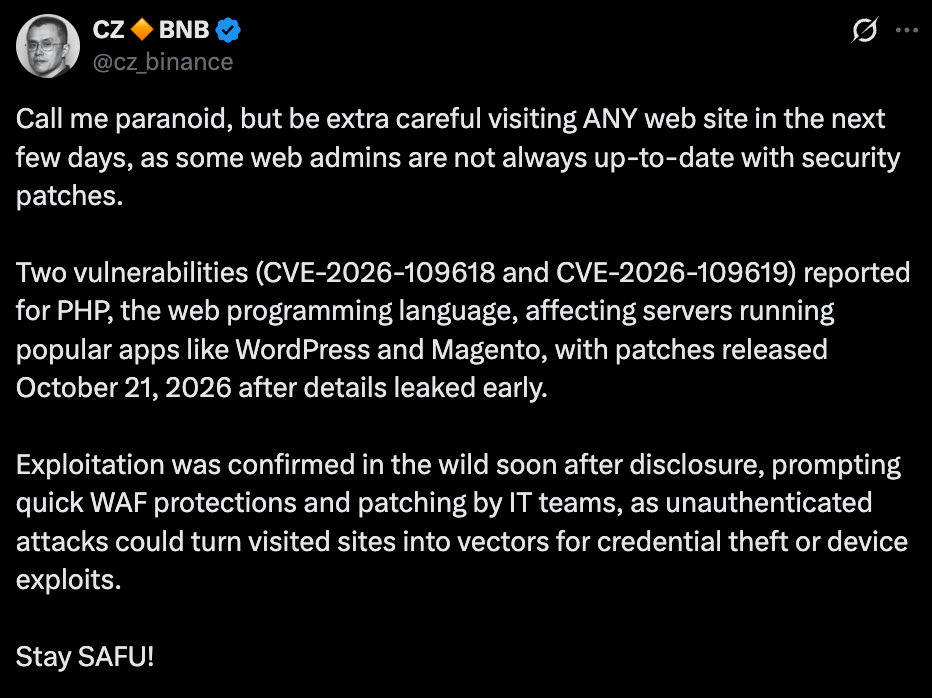
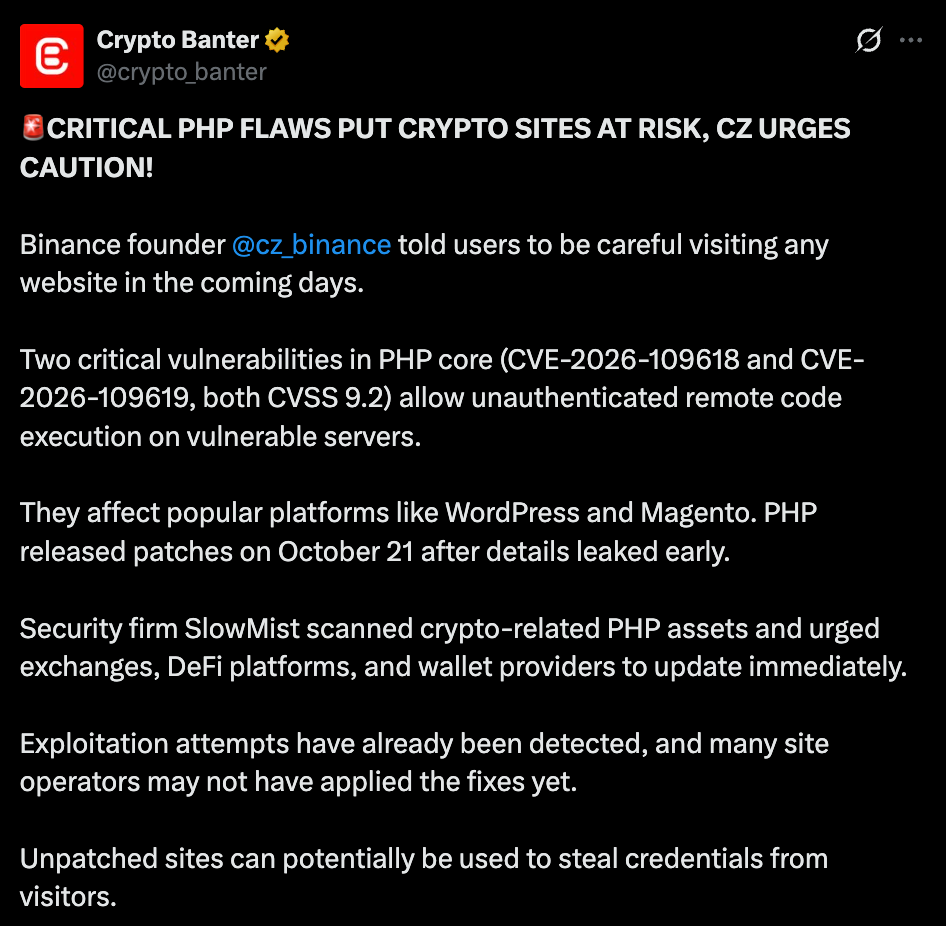
Crypto Banter also covered this news in its tweet on X, framing it as a risk for exchanges and wallets.
What Is the CZ PHP Warning Today?
The CZ PHP warning centers on CVE-2026-109618 and CVE-2026-109619, two bugs in a widely used web programming language.
CERT-EU’s advisory rates both at CVSS 9.2 and says each can allow unauthenticated remote code execution.
Each critical vulnerability works differently:
CVE
Flaw type
CVSS
CVE-2026-109618
Memory corruption during out-of-memory handling
9.2
CVE-2026-109619
Stale global state
9.2
CERT-EU adds that early proofs of concept have begun to circulate, raising the chance of exploitation in the wild.
Which PHP Versions Carry the Security Patch?
The PHP patch October 21 2026 covers four supported branches, andCISA urges organizations to update immediately.
Branch
Fixed version
8.5
8.5.12
8.4
8.4.27
8.3
8.3.36
8.2
8.2.35
Branches 8.1 and older no longer receive official updates, according to CERT-EU’s advisory.
Which PHP Vulnerability Crypto Exchanges Must Patch?
The Banter post says SlowMist scanned related PHP assets. The SlowMist PHP vulnerability alert, as described there, urged exchanges, DeFi platforms and wallet providers to update at once. SlowMist warns exchanges to update PHP before attackers reach them.
That also puts the PHP flaw wallet providers risk on the same list. Wallet security and crypto exchange security both depend on the servers behind each site.
CZ’s post names WordPress and Magento as apps on affected servers. A WordPress Magento PHP flaw matters only where admins have not updated, and a WordPress Magento PHP remote code execution attack needs no login.
Can Hackers Steal Crypto Credentials From Websites?
According to CZ, an unauthenticated attack could turn a visited site into a vector for credential theft or device exploits.
He also said exploitation was confirmed after disclosure, prompting quick WAF protection and patching by IT teams.
The Banter post adds that a PHP flaw crypto sites leave unpatched could be used against visitors.
That is why CZ warns users about visiting websites run by slow admins, and why the CZ PHP warning matters for logins.
How to Stay Safe From Crypto Website Hacks?
For web admins, the official guidance is short:
Update to one of the fixed versions listed above.
If patching is not possible, CERT-EU suggests isolating internet-facing apps until the fix is verified.
Temporary settings do not make an install safe, CERT-EU warns.
For everyday users, simple habits help:
The CZ Stay SAFU warning is his closing line, and it fits both groups.
Expert View: What Could This CZ PHP Warning Mean?
Analysts tracking crypto website security may read the alert as a reminder that routine patching matters as much as wallet design.
The CZ Binance founder security warning named no victim, and the sources cited here report no compromised platform.
Patch speed could decide which sites stay clean, though the outcome remains uncertain.
Disclaimer: This article is for information only, not financial or investment advice. Digital assets are volatile. Verify details with official sources.