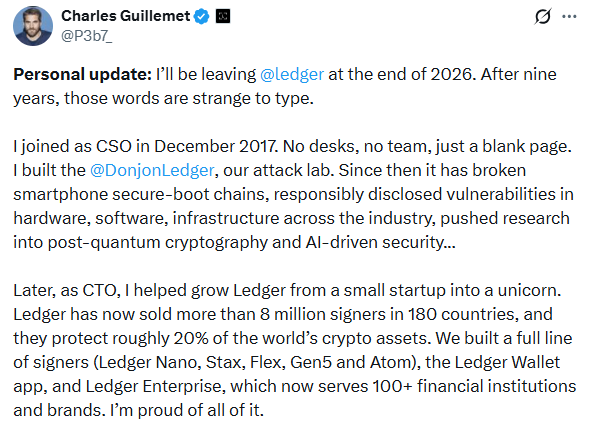
Ledger CTO Charles Guillemet has announced that he will leave the company at the end of 2026 after nine years, and he says the move was planned long before the latest security headlines. The
Ledger CTO Charles Guillemet has announced that he will leave the company at the end of 2026 after nine years, and he says the move was planned long before the latest security headlines.
The news arrives while Ledger is still looking into hardware wallets that were tampered with before they reached buyers, so many crypto users now want to know what the exit means for their coins.
Key Takeaways
Ledger CTO Charles Guillemet will leave at the end of 2026 after nine years at the company.
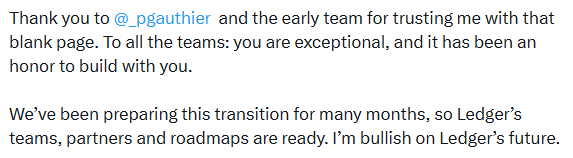
He called the move a planned transition that has been in the works for many months.
Ledger has confirmed that one affected device held an unauthorized implant, and its investigation is still running.
Ledger CEO Pascal Gauthier thanked Guillemet publicly and said he spent nine years protecting what matters.
Why Is Ledger CTO Charles Guillemet Leaving After Nine Years?
Guillemet shared the news in his own announcement, where he said, “We’ve been preparing this transition for many months.” He described it as a planned handover and not a sudden exit, and the details we reviewed do not name a successor yet.
What Ledger CEO Pascal Gauthier Said About the Exit
Ledger CEO Pascal Gauthier publicly thanked Ledger CTO Charles Guillemet in anofficial reply on X, saying that Guillemet built the Donjon attack lab from a blank page together with the team and spent nine years protecting what matters.
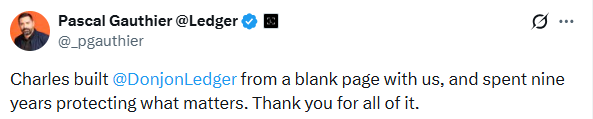
He closed his message with “Thank you for all of it,” which shows that the company is treating the exit as a friendly handover and not as a dispute.
Charles Guillemet at Ledger: From Security Chief to CTO
According to Charles, he joined the company in 2017 as Chief Security Officer and became Chief Technology Officer in 2019.
That path means he has worked on both the security and the engineering sides of a company that builds hardware wallets, which are small devices made to keep private keys offline and away from hackers.
Hardware Wallet Tampering Case Behind the Crypto News
In anofficial statement on X, the Ledger support team said that one affected user device contained an unauthorized hardware implant and that it was reaching out to impacted users as part of its investigation.
The reported goal of such an implant is to steal the recovery phrase, which is the set of secret words that can restore a wallet on any device, so anyone who learns those words can move the coins from anywhere in the world.
What Ledger Users Should Do Now
If you own a Ledger device, the safest habit is to buy only from the official store or a clearly approved seller and to keep the box sealed until you are ready to set it up.
Never type your recovery phrase into a website, an app, or a message, and never share it with anyone who contacts you. If you are unsure about where a device came from, it is wise to stop using it and move your funds to a new wallet with a fresh recovery phrase.
Disclaimer: This article is for information only and is not financial or investment advice. Crypto assets carry risk, including the loss of funds, so verify current details with official sources.