Policy6 min read
XRPL Wallets Move Inside Apps With Privy
Key Takeaways Privy lists XRP Ledger among the networks supported by its wallet infrastructure. Apps can connect XRPL wallet creation to their existing login and user-account flow. XRPL suppo
Paris-based Ledger is reviewing its reseller controls and anti-tampering protections after spyware planted in some wallets led to roughly $90 million in stolen crypto. Ledger describes the th
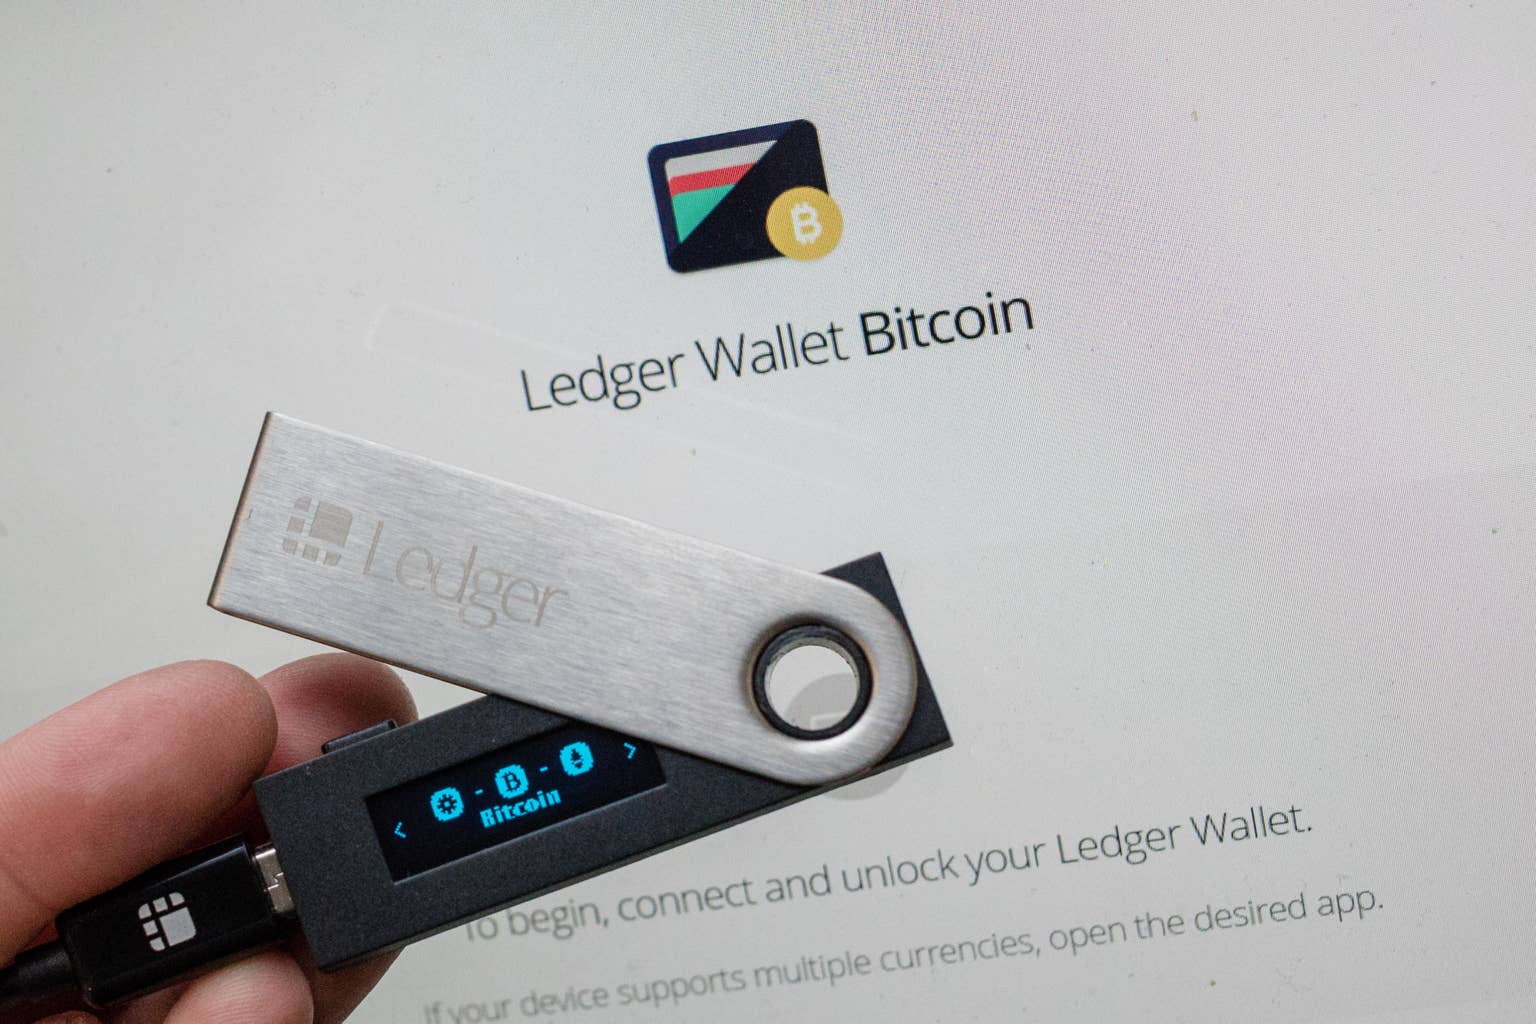
Paris-based Ledger is reviewing its reseller controls and anti-tampering protections after spyware planted in some wallets led to roughly $90 million in stolen crypto.
Ledger describes the thefts as a physical supply-chain attack, not a breach of its software or internal systems.
In an investigation update on X, Ledger said a spy chip inside devices sold by Southeast Asian reseller CryptoBilis read users' 24-word recovery phrases off the screen and sent them over a mobile network using an eSIM.
Ledger said the implant did not touch the secure element or alter transactions.
In a post on X, Mt. Gox's former CEO Mark Karpelès said he found a spy implant in an unused Ledger Flex bought at Singapore's airport.
Related: Dave Ramsey's investing advice falls short, study finds
Buyer Ben Yorke bought it from the airport and identified Metapod as the retailer. Ledger says every confirmed loss so far traces to CryptoBilis devices, and it has not verified a theft involving a wallet bought elsewhere.
Reports also surfaced of tampered devices bought from German retailer MediaMarkt. A MediaMarktSaturn spokesperson told Bloomberg the group has removed all of the manufacturer's products from its stores and online platforms.
In a post on X, CEO Pascal Gauthier said "Physical supply chain tampering is a risk for the whole industry." He added that Ledger is reviewing controls on direct sales and resellers.
“Some claims and figures circulating online are unverified. Scammers often try to take advantage of incidents like this. Rely only on official Ledger channels for updates,” he mentioned.
CTO Charles Guillemet asked users to send suspicious devices to Ledger. The company says its investigation into who tampered with the devices is ongoing.
“If you bought a Ledger signer from CryptoBilis and have not set it up, do not set it up. If you have set it up, transfer your assets promptly to a new signer with a new recovery phrase,” he alerted.
Galaxy Digital research put losses above $90 million. CoinDesk cited onchain estimates of up to $93.2 million across more than 300 wallets, with Tether freezing $10 million of USDT.
Ledger has not confirmed total victims or losses. It told CryptoBilis customers not to initialize unused devices, and those who already did to move funds to a new device with a fresh recovery phrase.