Cloud Platform Faces Credential Exposure Concerns The railway security breach has entered the crypto hack news cycle as of October 22, 2026. The cloud platform said an unauthorized party may
The railway security breach has entered the crypto hack news cycle as of October 22, 2026. The cloud platform said an unauthorized party may have accessed customer secrets. Separate on-chain data then flagged suspected wallet drains worth at least $369.3K.
Disclosure Points to Exposed Environment Variables
Railway published its official disclosure on October 21, 2026. It said it detected unusual activity in systems that store customer environment variables. These settings can hold API keys, which are access codes for software services, plus database logins.
According to the disclosure, an unauthorized third party may have read encrypted values, and some were decrypted. It believes the incident is part of a series of attacks on platform companies.
The goal, it says, is to compromise AI inference providers, which run AI models for apps. It has asked those upstream providers to revoke all keys as a precaution.
All deployments are paused during the investigation, so developers cannot release new versions. The platform says the railway security breach may affect only a subset of users. It still urges everyone to act and will email affected customers directly.
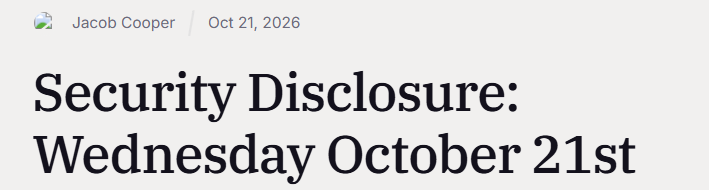
Source: Official Blog
On-Chain Data Flags Suspected Wallet Drains
A post on X dated October 22, 2026, shared tracking of a suspected attacker wallet. It moved at least $369.3K to HitBTC and other addresses. It also received funds from an address linked to the CryptoBillis Ledger Drainer, a tool that empties victim wallets.
The official disclosure does not mention any such transfers. That address has no confirmed link to the railway security breach. Readers should treat the figure as unverified.
HitBTC is a crypto exchange. On-chain trackers can follow transfers to its addresses because blockchains are public. A transfer alone, however, does not prove who owns the funds or how they were obtained.
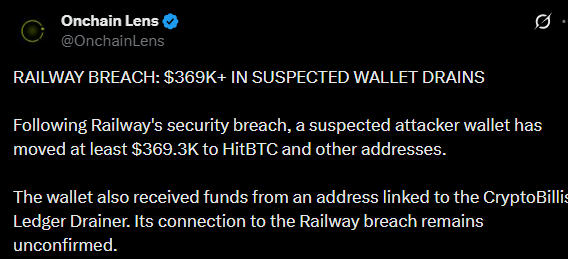
Source: X Post
Key Facts From the Incident So Far
Item
Detail
Source
Disclosure date
October 21, 2026
Company blog
Data at risk
Environment variables and API keys
Company blog
Platform status
Deployments paused.
Company blog
Suspected transfers
At least $369.3K to HitBTC
X post, October 22, 2026
Link to incident
Not confirmed
X post, October 22, 2026
Practical Steps for Affected Developers
The guidance after the railway security breach applies to every user:
Rotate all environment variables and API keys, which means replacing each stored secret.
Replace private registry credentials.
Review service logs for unusual activity.
CheckAmazon Web Services andGoogle Cloud access logs using the guides posted on October 22, 2026.
Follow the official status page for updates on when builds resume.
Expert Take: Why Secret Rotation Matters
Environment variables often hold keys with wide access. If a third party read them, rotating secrets limits further misuse. The step costs little compared with the risk of leaving old credentials active.
The on-chain figure needs more evidence before anyone ties it to the incident. A careful reading of the railway security breach separates confirmed facts from unconfirmed activity. Developers who build crypto apps on cloud platforms may also review how they store credentials.
Confirmed details will come from the status page and follow-up posts, including which accounts were affected. Until then, the wallet figure stays unverified. As of October 22, 2026, this crypto breach remains an evolving story in hack news.
YMYL Disclaimer: This article is for educational and informational purposes only. It does not offer financial advice, price predictions, or return guarantees. Readers should verify details through official sources before acting.