What the Team Revealed About the Bridge and Token Hit Crypto news update from the official @zilliqa account is out. The Zilliqa security breach update confirms that X-Bridge and some ZRC2 pro
What the Team Revealed About the Bridge and Token Hit
Crypto news update from the official @zilliqa account is out. The Zilliqa security breach update confirms that X-Bridge and some ZRC2 proxy contracts were affected, while native ZIL and the EVM chain were not.
The team posted the update in an X thread on Oct 27. It builds on a first alert from Oct 25.
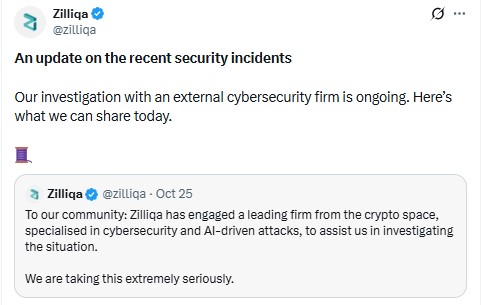
That earlier post said a leading crypto cybersecurity firm, skilled in AI-driven attacks, was helping with the probe. The investigation is still ongoing, and no root-cause report has been published.
Which Tokens and Pools Are Affected by the Incident?
According to the project, the affected tokens are zUSDT, SEED, kUSD, and Zoge. They sit in ZRC2 proxy contracts used by liquidity pools such as PlunderSwap.
A proxy contract points to the logic behind a token. Control over it can change how that token behaves, which is why these contracts matter.
Item
Status
Native ZIL
Not affected
EVM network
Not affected
X-Bridge
Suspended
zUSDT, SEED, kUSD, Zoge
Affected
Operational keys
Being rotated
X-Bridge stays suspended, and the team is rotating all operational keys. It is also working with exchanges and law enforcement. Users should avoid the bridge and the affected pools until further notice.
Still unconfirmed:
Why the CEO Exit Matters for the Zilliqa Security Breach
Alexander Zahnd, who became interim CEO in May 2025, has stepped down at his own request.
The Board now oversees the response directly. An external advisory firm focused on cybersecurity and governance supports it until a permanent leader is named.
This Zilliqa security breach update also says strategic partners, including Telecom Liechtenstein, will be briefed. The stated priorities are user fund safety and transparency.
How This Compares With Earlier Zilliqa Bridge Exploits
This is not the first scare. In Feb 2025, an attacker used flaws in new token manager contracts to mint zETH and zBNB without locking matching assets, as the official overview explains. The team paused and upgraded the contracts.
A separate 2026 case hit legacy transactions through a Ledger app signing flaw. The project’s incident page reports about 683 million ZIL stolen. It is a different issue from the bridge.
Past bridge exploit cases show why keys matter. Bridges hold large liquidity and depend on privileged access, so they draw attackers.
What Users and Liquidity Providers Should Do Now
Stay away from X-Bridge and the affected pools for now.
Ignore DMs offering recovery help, since crypto scams often follow incidents like this.
Use only the official X account and blog for updates.
Holders of the four tokens face price and liquidity risk until pools reopen. Exchanges may also pause deposits or withdrawals, so check each platform’s notice.
The Zilliqa security breach points to a serious but limited incident. Native ZIL is untouched, yet the bridge, four tokens, and the CEO seat are all affected. Method and losses remain unconfirmed, so watch official channels for the next crypto update.
Disclaimer: This article is for educational and informational purposes only and should not be considered financial or investment advice. Always conduct your own research before making investment decisions.