Google is building a custody service for crypto assets. The target group is banks and large financial institutions; retail investors are not on the list. It was presented on October 28, 2026
Google is building a custody service for crypto assets. The target group is banks and large financial institutions; retail investors are not on the list. It was presented on October 28, 2026 under the name Google Multi-Party Compute. The core is simple: the private key used to sign a transfer on a blockchain never sits complete in one place. It breaks into parts that are spread across separate compute environments, and a signature comes about only once enough parts work together. For your own coins, nothing changes today. The news matters for a different reason: the most common cause of very large losses in the crypto market is a key that falls into the wrong hands. Broken protocols and wrong views on price cost the market considerably less.
What Google Multi-Party Compute is and how a signature arises without a complete key
Multi-party computation, MPC for short, is a cryptographic method in which several participants jointly compute a result without any of them seeing the others' inputs. Applied to the custody of crypto assets: the private key is split into fragments instead of being copied and locked away in one place. Each fragment sits in a different environment, for instance at Google, on the institution's own hardware and with a third provider.
When a transfer is to be signed, these environments compute together. The complete key arises at no point, not even for a fraction of a second. That is the decisive difference from a classic vault, out of which a key is taken for use and locked away again afterwards. Steal one of the fragments and you hold nothing usable.
According to the report by CoinDesk, a policy check also runs on top of the fragments. Before every signature it verifies whether the operation matches the institution's rules. Such rules can be an upper limit on amounts, a list of permitted destination addresses, or the requirement that several departments approve. By Google's account, this check takes place in a sealed-off compute environment that the company calls Confidential Space.
Where the difference from a multisig account lies
Do not confuse MPC with a multisig account. With multisig the blockchain itself knows that several signatures are required, and each of them comes from its own full-fledged key. With MPC the blockchain sees only a single, entirely ordinary signature. The splitting happens beforehand and stays invisible from outside. That makes MPC independent of whether a blockchain supports multisig at all, and it explains why institutional custodians prefer the method.
Two of three parts suffice: how a signing threshold makes the theft of one fragment worthless
The number of fragments and the number of fragments needed for a signature can be set separately. Google names two examples: two of three participants, or five of seven. Such a threshold resolves two problems at once that otherwise work against each other in custody.
The first is theft. With a threshold of two out of three, an attacker needs two fragments from two different environments, and needs them at the same time. A single successful break-in gets him nowhere. The second problem is loss. If a fragment is destroyed because a data centre fails or a device is wrecked, two remain, and the holdings stay reachable. This is exactly where custody models with a single key fail time and again: securing against theft and securing against loss pull in opposite directions.
The higher the threshold, the safer and the less movable the holding becomes. Five of seven suits a reserve that is rarely touched. Two of three suits holdings that move daily. That an institution can run both in parallel matters more for operations than any single number.
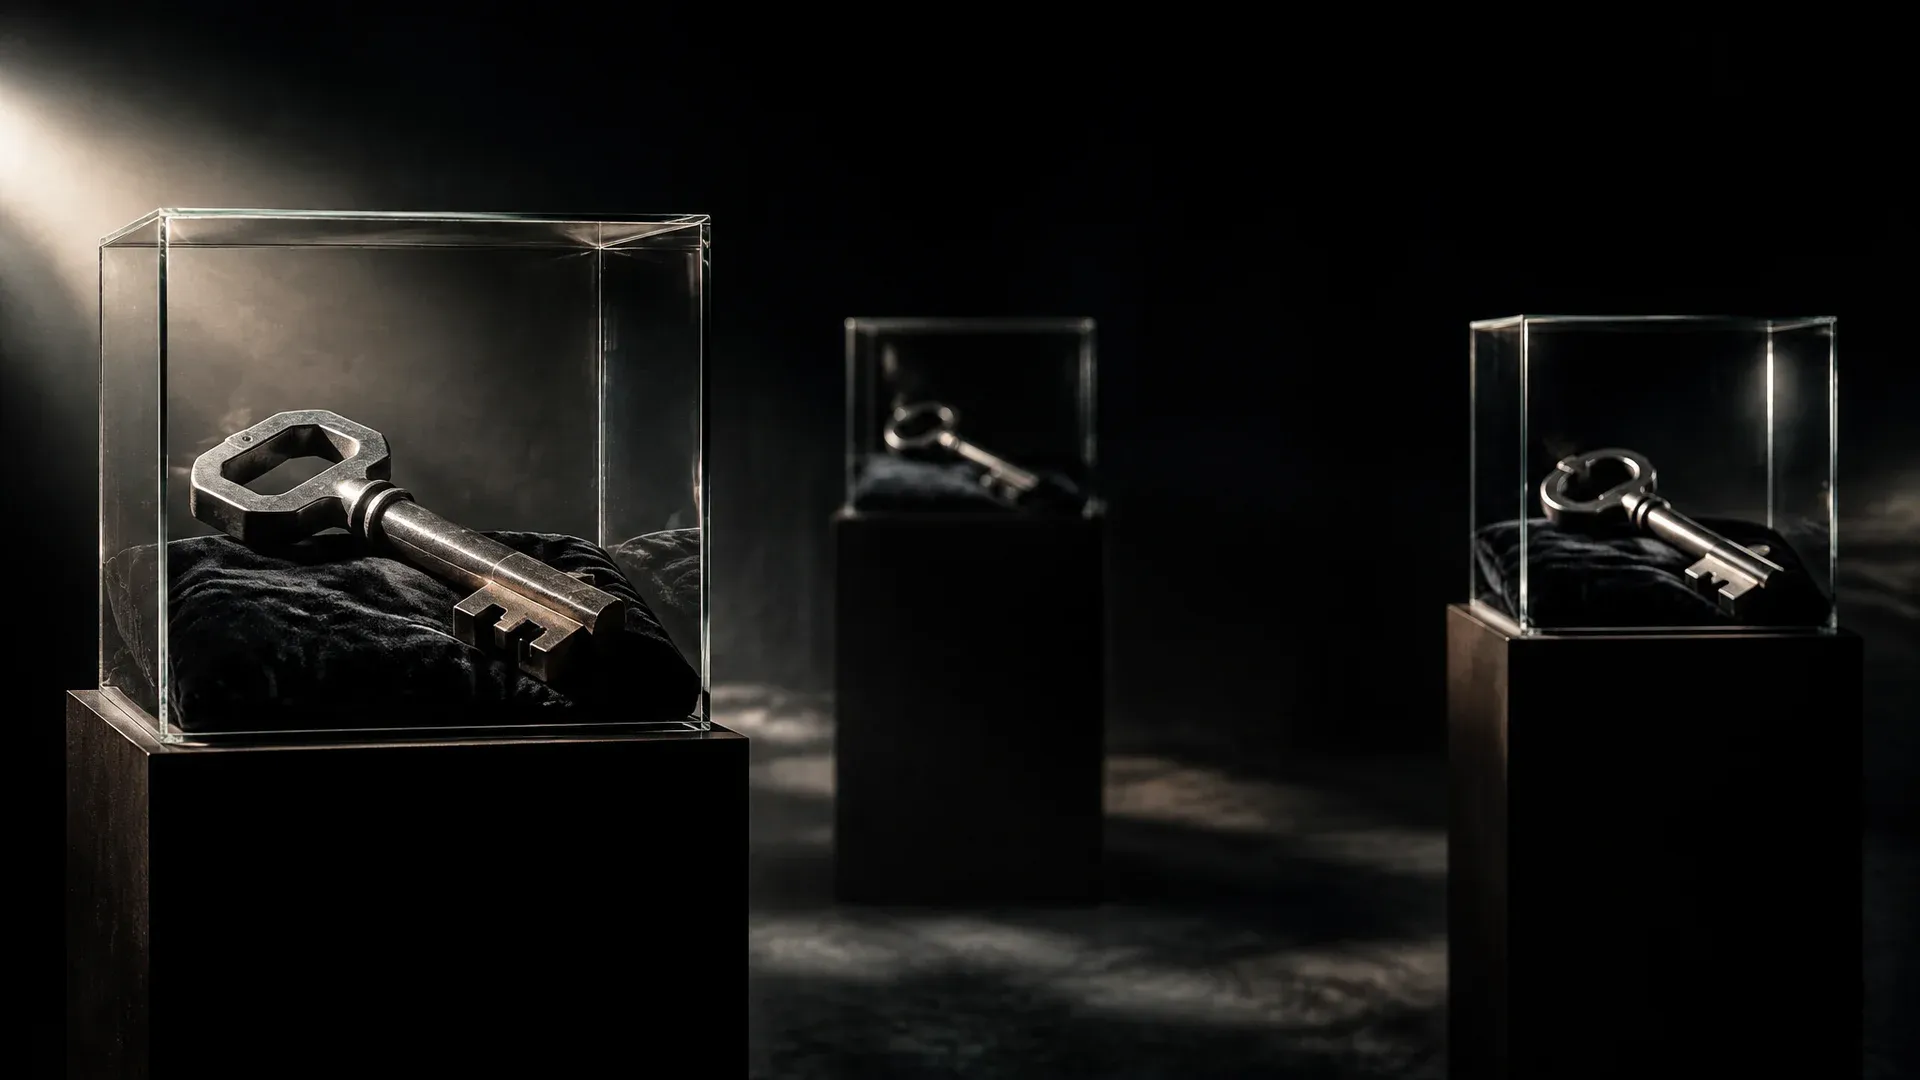
Two lit cases, three keys: a threshold of two out of three is enough for the signature, and the third fragment may fail.
A closed preview instead of a finished product: the roadmap to early 2027
What Google has presented is not yet a service an institution can book. The offering sits in a closed preview. Several development partners and, by Google's account, larger financial institutions as well are testing it; the company has named none of them. Commercial release is announced for early 2027. There are no prices so far.
For Google, the product is newer than the technology. Back in 2023 the company had described how customers could build MPC custody on its sealed-off compute environment themselves. What was missing was a finished custody service that Google operates and answers for itself. It is taking that step now.
A sober look helps in placing the timing: between a closed preview and a service onto which a European bank puts its customers' assets lie supervisory reviews, certifications and contracts. Do not count on finding Google's name in the small print of your brokerage account in 2027.
Compromised keys are the single largest cause of loss in the crypto market
Why a company of this size gets into key custody at all becomes clear from a look at the causes of loss. The public hack database of the analytics firm DeFiLlama lists 1,326 incidents from the period of June 19, 2011 to October 27, 2026. Taken together, $21.19 billion was lost in them. Of that, $8.96 billion falls to the category of compromised keys, spread across 162 incidents. That is 42.3 percent of the total sum and therefore more than for any other cause. cryptoticker.io compiled this analysis itself on October 29, 2026.
The problem has not grown smaller either. For the current year 2026, the same database already holds $721.1 million in losses from compromised keys; for the whole of 2025 it was $302.0 million. The CoinDesk report arrives at a similar magnitude by another route, citing an analysis by Chainalysis according to which 43.8 percent of the crypto assets stolen in 2024 traced back to compromised keys.
One insight follows, and it holds for you as much as for a bank: the most expensive mistake in this market is rarely a wrong view on price. It is the question of who holds the key.
ECDSA, Ed25519 and the open question of quantum-safe signatures
At general availability the service is to handle two signature methods. ECDSA is the method with which Bitcoin and Ethereum, among others, sign transfers. Ed25519 is used by blockchains such as Solana. With these two the service covers the bulk of today's relevant networks, but not everything.
The answer to quantum computers remains open. Google holds out the prospect of supporting quantum-safe signature methods later, once the blockchains adopt them. The company names no date for it, and the capability is not included in the scope of the preview. That is an honest framing, because the decision rests with the networks and not with a custodian.
How big the task is in the end is hinted at by a figure from the CoinDesk report: around 6.9 million Bitcoin are regarded as possibly vulnerable to future quantum attacks, because their public keys stand openly in the blockchain. This is no danger for tomorrow. It is a reason why custodians build their methods to be interchangeable.
What Alphabet does with its own holdings on Ethereum and Solana
One detail of the presentation deserves more attention than the product announcement itself. By Google's account, parent company Alphabet secures its own digital assets on Ethereum and Solana with the same technology. Which assets those are and how large the holdings turn out to be, the company has not disclosed.
Two things can be read from that without reading anything into it. First, one of the world's largest technology companies holds positions in these two networks at all. Second, it trusts its own method enough to secure them with it. That is no argument for buying and says nothing about prices. As an indication of how far the infrastructure for institutional holdings has matured, it serves nonetheless.
Rich Widmann, responsible for strategy in the digital assets business at Google Cloud, placed the move as follows according to CoinDesk: adoption and tokenisation of digital assets stand “at an inflection point”. Read as the assessment of a participant rather than a market forecast, the sentence fits the situation.
Separate paths instead of one place: the fragments of a key sit in different environments and never come together.
Fireblocks, Fordefi and BitGo: who serves the market for institutional custody today
Google is not entering an empty market. The company itself names Fireblocks, Fordefi and BitGo as providers that cover the securing and approval of transactions for institutions today. These firms have lived off precisely this task for years and know what the supervisors require.
What Google brings is no better method but a different starting position. Many banks run their systems in one of the large compute clouds anyway. If custody is available there as a building block, a separate contract with a specialist provider falls away. This very route has shifted other markets before.
What a cheaper custodian changes for you
For you it works through costs and through supply. The price has nothing to do with it. If custody becomes cheaper and easier for banks to run, the number of institutions that offer crypto assets at all grows. More providers mean pressure on fees and spreads. That is a slow effect over years, not an event around which to plan an entry.
MiCA and the supervisors: a technology provider is not an authorised crypto custodian
Here lies the misunderstanding that attaches itself to such reports. Google does not hold customer assets with this service. The company supplies the technology with which an institution controls its keys. The custodian remains the institution, and the liability therefore stays there too.
In the EU this role requires a licence. Anyone holding crypto assets for customers needs an authorisation as a crypto-asset service provider under the EU regulation MiCA. The national supervisory authority grants it and oversees the providers; authorised firms appear in a public register of the European supervisory authority ESMA. Banks and investment firms that are supervised anyway can notify the service instead of applying for a full authorisation. Among the obligations is that customer holdings are kept separate from the firm's own.
In practice that means: if the name of a technology company appears in a report, that tells you nothing about who has to answer for your coins. That question is answered by your provider's authorisation alone.
Custody at an exchange or in your own hands: the two questions that decide
Little carries over from a closed preview for banks to your own portfolio. This news does raise two questions for private holdings, though, and both can be answered today.
The first question is who holds the key. If your coins sit at an exchange, the exchange holds the key and you hold a claim against it. So check whether your provider carries an authorisation under MiCA, whether it keeps customer holdings separate and what it writes about its custody. A firm that says nothing about its key management has not answered this question for you.
The second question is whether you want to hold the key yourself. Then the responsibility rests with you, and there is no firm that irons out a mistake. A hardware wallet keeps the key in a device that is not attached to the network; a software wallet is more convenient and lives with the risk of the device it runs on. The split into several parts that Google is building for banks can be reproduced on a small scale, by the way: spreading your wallet's recovery words across two separate places works with the same idea, only by hand.
How to recognise a sound custody disclosure
A solid disclosure names three things: who technically controls the keys, under which supervision the firm stands, and what happens to the holdings in the event of insolvency. If one of these points is missing, the statement is advertising and not information.
Google custody: until 2027 custody stays your job
The announcement shifts the infrastructure behind the market, not the situation in your portfolio. Three steps are worth taking nonetheless:
- Look up your provider's authorisation. Clarify whether your trading venue or broker is authorised under MiCA and which obligations come with it.
- Think your own custody through once. Decide for every part of your holdings whether it should sit with a custodian or with you. On the device side, a look at current hardware wallets in comparison helps.
- Put the custody question before the fee question. Anyone choosing between trading venues should include custody in the calculation. Which firms operate with an authorisation in the EU is shown by our list of regulated crypto exchanges.
The figures on the causes of loss in this article are based on the public hack database of DeFiLlama.
(As of October 29, 2026. This article is not investment advice. Prices and fee structures change; check the terms with the provider before you buy.)