Ledger (@Ledger) says hardware wallets sold by the Southeast Asian reseller CryptoBilis were modified to capture users' recovery phrases and send them to attackers over a cellular network. Th
Ledger (@Ledger) says hardware wallets sold by the Southeast Asian reseller CryptoBilis were modified to capture users' recovery phrases and send them to attackers over a cellular network. The company says the secure chip and the transaction signing process were not affected.
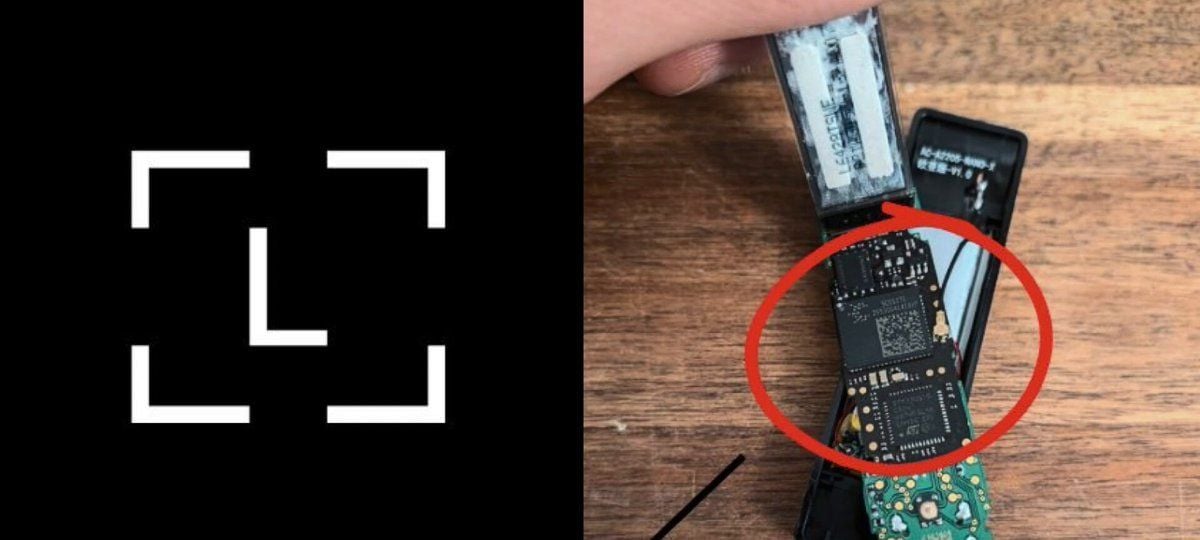
Ledger Donjon, the company's security research team, found that the implants used a microcontroller to decode the 24-word phrases displayed during setup and transmitted the data over LTE networks using an embedded SIM (eSIM). Ledger said the component operated independently and did not alter the device's Secure Element or operating system. It also did not interfere with transaction signing.
How the attack worked
The implant sits inside the device casing. Researchers cited by Tech Times say it is wired into the internal data channel that carries information to the screen, which lets it read the recovery phrase as it is displayed. Ledger says its Genuine Check cannot rule out this type of physical tampering. That means a modified device can look and behave like a normal one.
The incident points to a supply chain problem rather than a flaw in Ledger's cryptography. A device can keep its software defences intact while an added physical component exposes the words that can restore the wallet.
Losses and guidance for users
The scale of the losses is not confirmed by Ledger. All confirmed losses disclosed on Oct. 9 have been linked to devices distributed through CryptoBilis, Ledger said, but no affected-user total or overall loss figure has been confirmed. Estimates from outside the company are high. On-chain forensics firm Bitquery put losses above $90 million across at least six blockchain networks, with Tron accounting for roughly $70.5 million and Bitcoin and Ethereum making up most of the remainder. Other outlets have reported figures from $86 million to about $93 million, so the total may exceed $100 million only if further thefts are linked to the same devices.
CryptoBilis has suspended Ledger product sales. Ledger advised customers who bought uninitialized devices through the distributor not to set them up. Customers who already initialized an affected device should move their assets to a new device with a newly generated recovery phrase. Restoring the old phrase on new hardware would not help, because the phrase itself may already be exposed.
Ledger has also directed concerned customers who bought devices elsewhere to an inspection guide, which warns that opening a device could damage it and advises users to back up their recovery phrases first. Buying directly from the manufacturer remains the most reliable way to avoid tampered hardware.
Sources
Cointelegraph: Ledger details LTE-enabled spy implants in wallets sold by CryptoBilis
TokenPost: Ledger confirms CryptoBilis wallets were altered to expose recovery phrases
Tech Times: Ledger hardware wallet supply chain attack and Genuine Check limits