On November 16, hackers used Optimizely Web to send malware JavaScript code to visitors of websites of 178 companies. Well-known companies, such as Zoom, BBC, CNN, Salesforce, GitLab, HSBC, a
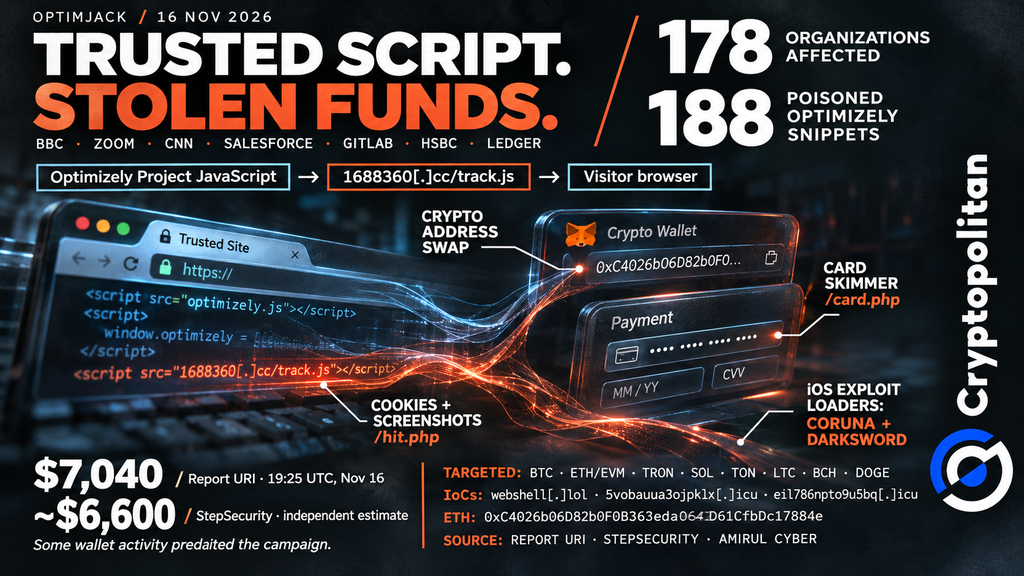
On November 16, hackers used Optimizely Web to send malware JavaScript code to visitors of websites of 178 companies. Well-known companies, such as Zoom, BBC, CNN, Salesforce, GitLab, HSBC, and Ledger, were among the victims.
Report URI has analyzed 1,611 Optimizely scripts and found infected code in 188 of them. The attackers didn’t need to hack each of the companies’ websites since the infected code came from the trusted content delivery network (CDN) of Optimizely and was able to run in the visitors’ browsers. Researcher Amirul Cyber named the hack OPTIMJACK.
Trusted code that stopped being trustworthy
By taking advantage of the Project JavaScript field in Optimizely, the hacker was able to run 1688360[.]cc/track.js. After that, the code was able to function with the same rights as those the host website had.
According to Optimizely’s permissions documentation, only administrators and owners of projects may alter snippets. It remains unclear how the basic security protections of Optimizely were bypassed. Even the company’s marketing and login pages were launching the code.
Researcher Scott Helme of Report URI warned:
The important lesson here is that trusted JavaScript doesn’t always remain trustworthy.
One script, four jobs
The malicious software sought out cryptocurrency wallets and substituted them with wallets belonging to the hacker. The malware has been said to concentrate on Bitcoin, Ether, and various other EVM chains, TRON, Solana, TON, Litecoin, Bitcoin Cash, and Dogecoin. The substitutions could be visible in website content, online forms, copy-pasted addresses, as well as outgoing network requests.
The attack went beyond cryptocurrency theft. The same script captured payment-card details and sent them to /card.php. It also collected readable cookies and page screenshots, which were sent to /hit.php, according to Report URI. On iPhones and iPads, separate .icu domains delivered code linked to the Coruna and DarkSword exploit kits.
OPTIMJACK Attack: How Hijacked Optimizely Scripts Hit 178 Sites
Roughly $7,040, and plenty still unknown
By 19:25 UTC on November 16, Report URI had traced about $7,040 in receipts to wallets linked to the malicious Optimizely scripts. StepSecurity estimated a lower total of roughly $6,600. Its review found that four of the eight wallets had received nothing. Some transactions also took place before the November 16 attack.
None of the estimates have established how much was actually stolen during the attack. Researchers are still in the process of identifying who was behind it. They also can’t provide the figures regarding how many payment cards, browsers, and iOS devices were affected in the attack. By the end of November 16, the majority of the infected Optimizely scripts had been deleted.
Earlier infections share the same plumbing
The Optimizely attack was not the only case involving infected third-party scripts that week. Hudson Rock traced similar infections between November 13 and 16. They involved scripts from Kissmetrics, StorifyMe and Minute Media. Websites including Security Bank and Fox Sports loaded a malicious script called webshell[.]lol/get.js.
The shared infrastructure suggests a connection between the incidents. However, researchers have not established how each provider was compromised or who was responsible.
Where the browser defenses failed
Not every website that got infected let the malware operate properly. Amirul Cyber recognized two samples of pages where the Content Security Policy (CSP) blocked the attacker’s script.
CSP limits the sources a browser can load code from. Optimizely’s guidance includes settings such as strict-dynamic and optional unsafe-eval, among others, but they have to be configured very carefully.
The PCI Security Standards Council mandates that approved scripts should be loaded and checked for integrity and tampering, as per requirements 6.4.3 and 11.6.1, when it comes to online payments.
A third-party problem bigger than one vendor
The World Economic Forum found 65% of large companies considered supply-chain vulnerabilities their biggest resilience challenge, up from 54% in 2025.
Verizon linked third parties to 48% of breaches. TRM Labs found infrastructure compromises caused roughly 76% of crypto-hack losses in H1 2026 despite representing just 15% of incidents.
OPTIMJACK shows how visitors can face theft even when a website’s own servers remain secure.
The smartest crypto minds already read our newsletter. Want in? Join them.