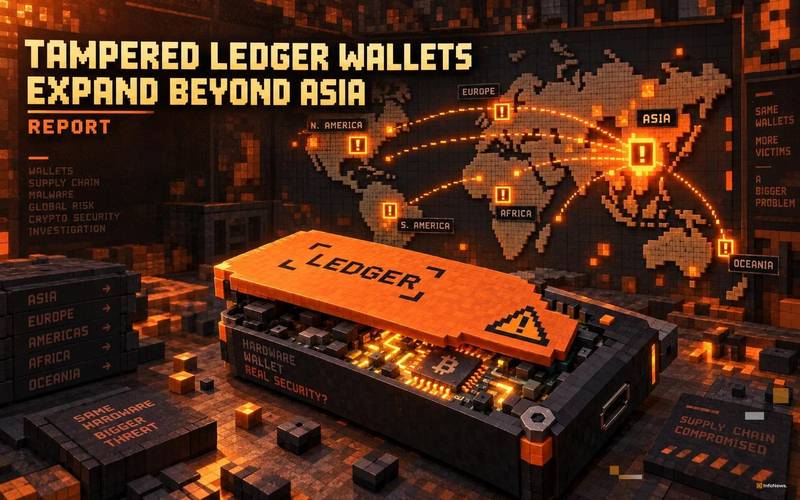
Reports indicate that tampered Ledger hardware wallets, previously concentrated in Asian markets, are now surfacing in regions beyond Asia, raising fresh concerns about the integrity of the h
Reports indicate that tampered Ledger hardware wallets, previously concentrated in Asian markets, are now surfacing in regions beyond Asia, raising fresh concerns about the integrity of the hardware wallet supply chain and the security of users who purchase devices through unofficial channels.
The reported geographic expansion has not been independently verified, and no official incident count, specific destination markets, or confirmed losses have been disclosed. The claims should be treated as unconfirmed reports until Ledger or a credible security researcher publishes primary documentation. Buyers in any region who acquired a Ledger device outside of Ledger's official store or authorized resellers should treat the report as a prompt to review their device's authenticity. For related coverage, see Coinme to Shut Down Crypto Kiosks in $2.5M Settlement.
Why Tampered Devices Are a Distinct Threat
A tampered hardware wallet is a fundamentally different risk from a phishing attack or a software vulnerability. Physical tampering can compromise a device before a user ever powers it on, making standard software security practices insufficient. The device may generate a seed phrase that an attacker already knows, effectively handing over control of every wallet the victim creates. For related coverage, see Bitcoin, Ethereum & Solana ETFs Post Negative October.
The risk is not theoretical. Investigators confirmed an unauthorized hardware implant in a customer's Ledger device, establishing that physical supply-chain attacks against Ledger hardware have occurred in practice. That case underscored that tampered units can pass casual inspection. Earlier, a reseller-level compromise also drew attention when Binance's then-CEO urged users to quarantine wallets after an $86 million Ledger reseller hack.
A tampered device attack is particularly dangerous for Bitcoin holders because Bitcoin transactions are irreversible. Once funds are swept by an attacker who controls the underlying seed, recovery is not possible through any customer support channel.
What Buyers Should Check Before Using Any Ledger Device
The reported expansion beyond Asia means the population of potentially at-risk buyers is wider than earlier warnings suggested. Ledger's official guidance remains the authoritative reference for verification; users should not rely on third-party summaries, including this article, as a substitute for consulting Ledger's published authenticity-check documentation directly.
As a starting framework, buyers should confirm three things. First, the device must have been purchased directly from Ledger's official website or a verified reseller listed on Ledger's site. Second, the packaging seal and holographic labels should show no signs of opening or resealing. Third, and most critically, the Ledger device itself should never arrive with a pre-filled recovery phrase; any device that ships with a seed phrase or asks the user to enter one provided externally is compromised.
During first setup, the genuine Ledger Live application cryptographically verifies the device's firmware and secure element. Users should complete this check and confirm the device passes before sending any funds. Any setup flow that bypasses Ledger Live or requests a recovery phrase entry should be treated as an active attack. Ledger previously described a wallet-draining incident as limited in scope, but supply-chain attacks scale differently from software exploits because each tampered unit creates an independent, persistent compromise.
WHAT TO KNOW
- Unconfirmed reports suggest tampered Ledger hardware wallets are appearing in markets outside Asia; no verified incident count or specific countries have been disclosed.
- Only purchase Ledger devices through Ledger's official website or its verified reseller list, and verify firmware authenticity through Ledger Live before depositing any funds.
For Bitcoin holders, the hardware wallet remains one of the strongest links in a self-custody security model, but only when the device itself has not been altered. A compromised device inverts that security entirely, converting a supposed safe into an open vault. Until the scope of the reported expansion is clarified by primary sources, users outside Asia who received Ledger devices through informal channels should treat verification as mandatory, not optional.
Additional source references: source document 1.
Disclaimer: This article is for informational purposes only and does not constitute financial or investment advice. Cryptocurrency and digital asset markets carry significant risk. Always do your own research before making decisions.
Bitcoininfonews first published the article titled Tampered Ledger Wallets Expand Beyond Asia: Report.