Hardware wallet vendor Trezor says it is tightening its distribution network after reports of malicious hardware implants discovered in devices sold by a Southeast Asian reseller under rival
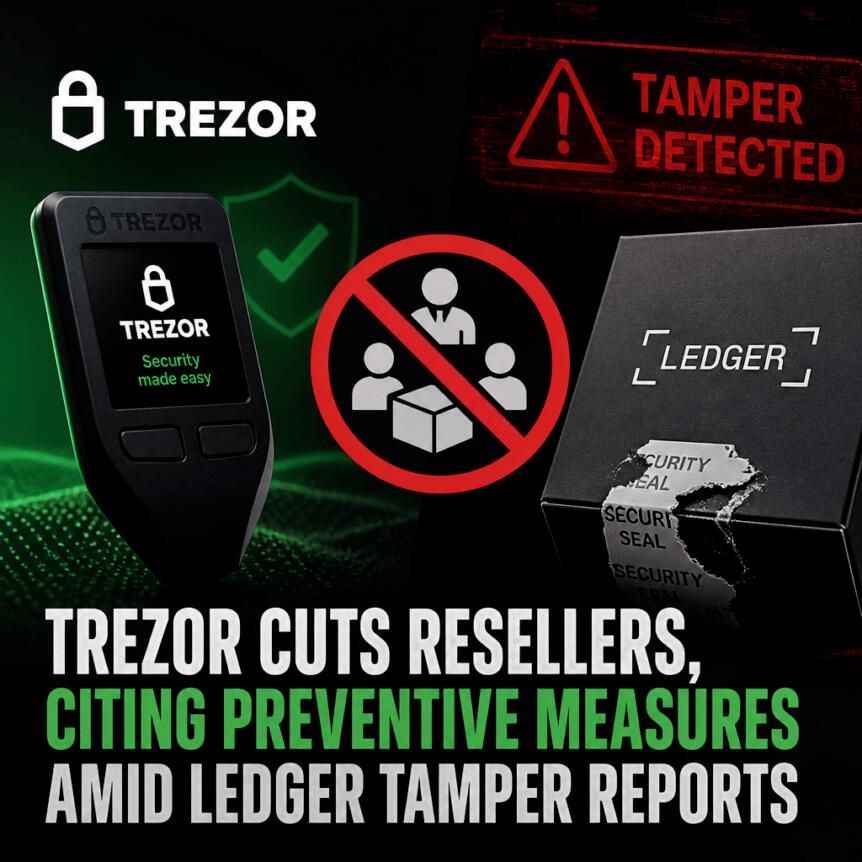
Hardware wallet vendor Trezor says it is tightening its distribution network after reports of malicious hardware implants discovered in devices sold by a Southeast Asian reseller under rival brand Ledger. The company’s move comes amid heightened scrutiny of how offline wallets can be compromised before they ever reach users.
In posts on X, Trezor said there is “not a single piece of evidence” that its own devices have been compromised. Still, the company plans to reduce the number of its resellers as a precaution, citing “recent supply-chain incidents.”
Key takeaways
- Trezor says it has found no evidence that its devices have been compromised, even as it responds to reports involving Ledger wallets.
- The company is reducing reseller coverage and will stop shipping Trezor devices to certain authorized partners starting Tuesday.
- Ledger confirmed unauthorized implants in at least one device purchased via CryptoBilis, a reseller in Southeast Asia.
- Research estimates shared publicly suggests affected user losses could range between $72 million and $86 million, though Ledger has not confirmed totals.
- Trezor advises buyers to purchase directly from the manufacturer and to verify that device seals remain intact; it also recommends multisignature setups for added resilience.
Trezor denies compromise, then changes its reseller strategy
Trezor’s response follows a wave of attention on hardware wallet supply-chain risks. While the company pushed back on claims that its own products were affected, it acknowledged the broader pattern: attackers appear to be finding ways to interfere with devices before customers ever receive them.
According to Trezor’s Tuesday X statement, the company is taking “a preventive step, taken out of an abundance of caution.” Trezor said it has “not a single piece of evidence” showing that its devices have been compromised.
Danny Sanders, Trezor’s chief commercial officer, added that specific resellers had been informed they would be removed from Trezor’s list of authorized entities starting Jan. 1. Sanders also stated that Trezor would halt shipments of Trezor devices to those partners beginning Tuesday.
The underlying message is straightforward: even without evidence of compromise, Trezor is attempting to shrink the number of potential handoff points between factory and end user.
Ledger’s implant findings set off wider concern
Trezor’s announcement arrived days after Ledger confirmed unauthorized hardware implant losses tied to at least one device purchased by a Southeast Asian reseller. In reporting earlier this week, Cointelegraph noted that Ledger said it found at least one of its devices contained an unauthorized implant and that the incident could result in losses running into the millions.
Those affected units were sold by CryptoBilis, and the reported behavior involved capturing recovery phrases and transmitting them over cellular networks. In this type of attack, the goal is not to alter the wallet’s firmware in a way that typical integrity checks would easily catch, but to capture sensitive information during user interactions.
Why Trezor says its defenses were not bypassed in the same way
Trezor’s spokesperson told Cointelegraph that the company’s existing checks are designed to catch counterfeit devices and modified firmware. The spokesperson also addressed the reported Ledger implant method, saying it works differently from what Trezor has detected on its own devices.
In the company’s description, the implant discovered in a device bought from CryptoBilis “works differently” and is a “unique way of tampering” that does not modify firmware. Instead, it reads information shown on the screen and later transmits that data to the attacker.
Trezor said it had not seen this specific type of attack on Trezor devices in the real world. That distinction matters for users because it suggests that not all “hardware wallet attacks” are identical: the same high-level supply-chain threat can manifest through different technical mechanisms, and defenses tuned to one behavior may not address another.
Retailers and resellers respond; users face uncertainty on losses
During the investigation into the Ledger-related incident, CryptoBilis—an authorized Trezor reseller—suspended all hardware wallet sales. Separately, Cointelegraph reported that the parent company of European electronics retailer MediaMarkt removed all Ledger products from both physical stores and online platforms “as a precautionary measure.”
While the hardware-wallet incident continues to be investigated, the market question for users is how widespread the compromise is and how much value may have been affected. In the source discussion, blockchain investigators had publicly suggested an estimated loss range of between $72 million and $86 million. However, Ledger told Cointelegraph it had not confirmed the total number of affected users or the overall value lost.
With totals still unverified, the practical takeaway for end users is that hardware-wallet supply-chain risk is shifting from a theoretical concern to an active, ongoing operational problem—one that involves resellers, packaging integrity, and how devices behave once they reach a buyer.
What Trezor recommends users do next
Trezor’s spokesperson advised users to buy devices directly from the company and to check that the seal on the packaging remains intact. The company also suggested users consider a multisignature wallet approach—specifically using devices from different makers—so that one potentially compromised device cannot unilaterally move funds.
These recommendations aim to reduce the likelihood of purchasing a tampered unit and to limit the damage even if a single device were somehow compromised.
Trezor’s decision to reduce reseller coverage highlights a key tension in the hardware wallet ecosystem: users want broad availability, but security benefits when fewer parties handle devices between manufacturing and delivery. What remains uncertain is how far the distribution changes will go across the industry, and whether regulators, retailers, and wallet makers will align on new minimum security requirements for packaging, authentication, and reseller vetting.
This article was originally published as Trezor Cuts Resellers, Citing Preventive Measures Amid Ledger Tamper Reports on Crypto Breaking News – your trusted source for crypto news, Bitcoin news, and blockchain updates.