Connecting a wallet to an application does not let that application move tokens. It reveals the selected public address and allows the application to read public information associated with i
Connecting a wallet to an application does not let that application move tokens. It reveals the selected public address and allows the application to read public information associated with it, such as its balance. A token approval is a separate action. It gives a named spender permission to move a particular token from that address, up to a stated limit. The spender is usually a smart contract, which is software that carries out an application’s instructions. A later transfer uses the permission. Revocation removes any unused authority but cannot reverse a completed transfer.
Approval phishing exploits that legitimate permission instead of necessarily stealing a recovery phrase or private key. Chainalysis says more than 7,000 leads processed during Operation Spincaster helped investigators pursue cases involving $162 million in losses. A normal approval may be needed when an application exchanges or deposits a token on the user’s behalf. The risk depends on what was authorized, which spender received the permission, how much of the token it could move, and whether it later exercised that authority.
Connection Does Not Grant Token Access
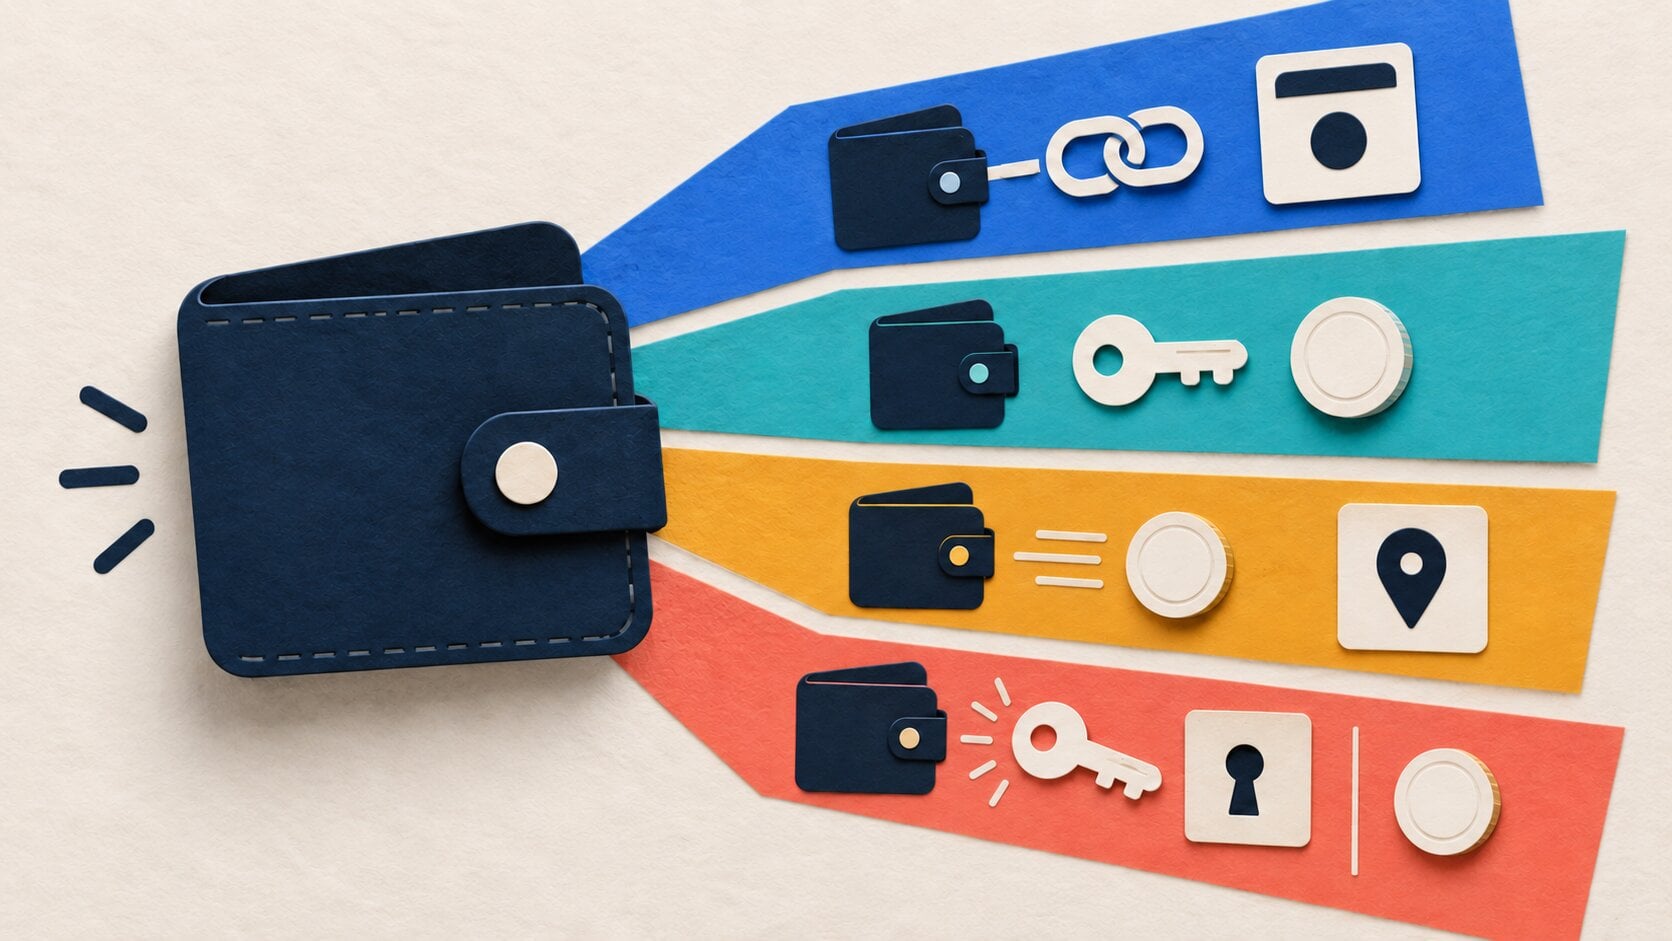
Infographic by the author
Incident reports often compress several actions into one line: a wallet connected, the user signed, and the assets moved. Each verb requires separate evidence. Understanding this often starts with looking at resources such asAlphaWire's crypto news, which covers many of the different elements of sending crypto and managing connections. This kind of site can provide a strong foundational understanding of the crypto world, from which users can build their interactions.
A user may first identify a signature, then add the token, authorized spender, allowance, completed transfer, or revocation as those details are confirmed. Coverage published before that transaction trail is complete may describe only one part of the sequence. “Connected” means the application learned which public address the user selected. “Approved” means the wallet owner granted a spender permission over a particular token. “Transferred” means the spender used that permission. “Revoked” means any remaining authority was removed. A report confirming only the first action has not established the other three. An unchanged balance does not prove that no permission remains open because the spender may not have used it yet. The decisive facts are the token, the spender, the amount authorized, and the order in which approval, transfer, and revocation were recorded.
A connection normally lets an application recognize the selected address and prepare actions for the wallet to review. The wallet owner still has to approve or reject those actions. Disconnecting later can end that direct connection, but it does not alter a token allowance already recorded on the blockchain. Closing a tab or removing a site from a wallet’s connected-app list therefore cannot replace revocation. The approval remains associated with the token and authorized spender until its terms end, its amount is used, or the wallet owner changes it.
Four Actions with Different Consequences
As described above, a wallet incident may contain four separate actions:
Connect: The application receives the selected public address. It can read public blockchain data associated with that address, but connection alone creates no token allowance.
Approve: The wallet owner authorizes one spender to move tokens within a specified limit. No token normally moves at this point.
Transfer: The spender uses some or all of that allowance. Tokens leave the wallet only when this separate action succeeds.
Revoke: The wallet owner removes or reduces the unused allowance. The spender then loses the corresponding permission for future transfers.
Wallets also request signatures for purposes that do not create token approvals, including proving control of an address. A report saying that someone “signed a message” has not established that a token allowance changed. Some signed requests authorize token access; others do not. The contents of the request and the resulting blockchain record determine what happened. A transfer can also be approved and completed within one workflow, but the permission and movement remain separate actions with different consequences.
Why an Approval Can Remain Active
A limited approval sets a maximum amount; it is not always a one-use permission. If the spender uses only part of the allowance, the remainder may still be available. A finite allowance normally falls as approved transfers use it. Once it reaches zero, another transfer requires a new approval. A large continuing approval can remain open until the wallet owner changes it. Some signed approvals include a deadline, but ordinary token allowances do not expire automatically.
The practical check is specific: identify the token, spender, and remaining allowance. An unfamiliar contract address may be difficult to recognize from its label alone, so the recorded address matters more than a shortened or incomplete name. The order of events also matters. A revocation recorded after a transfer did not prevent that earlier movement, even if the two actions occurred close together.
What Revocation Cannot Undo
Revocation works on future authority. If the allowance is still unused, removing it prevents that spender from relying on the same permission later. If a transfer has already been confirmed, revocation cannot roll it back. A July 2026 Secjuice analysis describes the same boundary and notes that revocation can become a race when an attacker already holds a signed permission.
Four factual questions separate most wallet-approval incidents. Was the wallet only connected? Which token, spender, and amount were approved? Did the spender complete a transfer? Was the remaining allowance revoked before another transfer? A confirmed connection answers only the first question. A confirmed approval establishes authority but not movement. The transfer shows what left, and the timing of revocation determines whether any unused authority was removed soon enough.
Disclaimer: This article is provided for informational purposes only. It is not offered or intended to be used as legal, tax, investment, financial, or other advice.