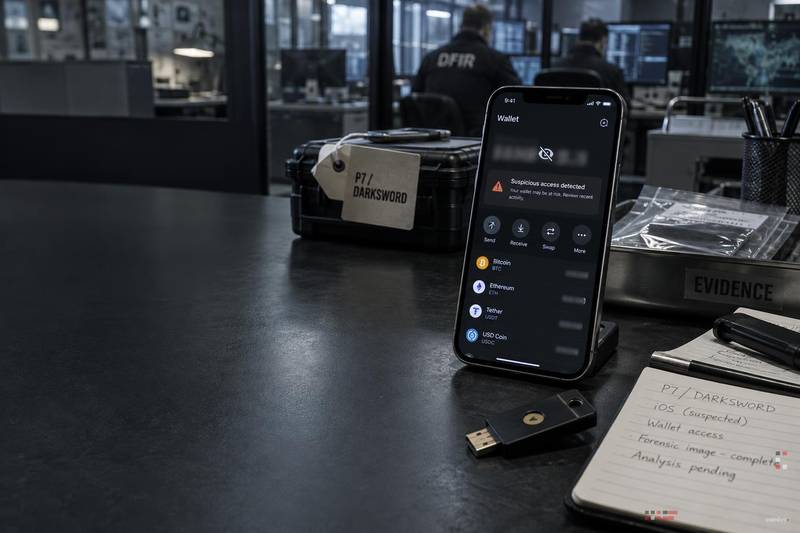
Security firm iVerify has identified an iPhone spyware strain called P7 DarkSword that actively scans for crypto wallet applications and extracts data from the imToken wallet on compromised d
Security firm iVerify has identified an iPhone spyware strain called P7 DarkSword that actively scans for crypto wallet applications and extracts data from the imToken wallet on compromised devices, raising urgent concerns for mobile crypto users.
KEY POINTS
- iVerify discovered spyware designated P7 DarkSword targeting compromised iPhones
- The malware scans for crypto wallet apps and extracts imToken wallet data
- Only devices already compromised are affected; the attack is not a general iOS vulnerability
iVerify Identifies P7 DarkSword on Compromised iPhones
iVerify, a mobile security firm specializing in iPhone threat detection, published findings on P7 DarkSword, a spyware strain designed to operate silently on iPhones that have already been compromised. The discovery is notable because it demonstrates targeted financial intent: the malware goes beyond generic data harvesting and specifically hunts for cryptocurrency wallet software. For related coverage, see Crypto CLARITY Act Senate Vote: What Happens Next.
The threat is not a zero-day exploit affecting all iPhones. P7 DarkSword requires the target device to already be compromised before it can operate, a distinction iVerify emphasizes in its report. For users who store crypto assets on mobile devices, that framing offers limited reassurance given how frequently spyware is deployed via phishing, malicious profiles, or supply-chain attacks on device management tools. Earlier this year, a supply-chain investigation involving Ledger highlighted how hardware and software touchpoints across the crypto ecosystem remain active attack surfaces. For related coverage, see Altcoin Gains 53% as Bitcoin Holds Near $83,000.
How P7 DarkSword Targets Wallet Apps and imToken Data
Wallet-App Scanning
Per CryptoSlate's reporting on the iVerify findings, P7 DarkSword scans the compromised iPhone for installed crypto wallet applications. The malware cycles through this scanning behavior repeatedly, checking for wallet app presence at frequent intervals. This persistent polling suggests the spyware is designed to catch wallet installations that may occur after initial compromise, not just at the moment of infection. For related coverage, see Metaplanet Sold 10,000 BTC, Bought 11,000 at 9.3% Higher Price.
Among the wallet apps targeted, iVerify specifically identified imToken as a named extraction target. imToken is a widely used self-custody wallet supporting Ethereum and multiple EVM-compatible chains. Data extracted from a wallet app on a compromised device could include account identifiers, transaction history, or locally cached credentials depending on how the wallet stores information. The practical risk is significant: wallet data from a compromised device may be sufficient to facilitate unauthorized access or targeted social engineering.
Security Implications for iPhone-Based Crypto Users
The finding reinforces a narrower but serious risk: iPhones running crypto wallet apps are not immune to targeted financial spyware once device integrity is lost. Users relying on mobile wallets like imToken should treat any device with a history of unusual behavior, unverified profile installations, or MDM enrollment as potentially compromised. Treating wallet data on such devices as exposed is the conservative and appropriate response given iVerify's report.
iVerify's research adds to a growing body of evidence that spyware operators are adapting toolsets to prioritize financial application data. Separately, security researchers have flagged protocol-level vulnerabilities as another attack vector; a flaw in the XRP Ledger earlier demonstrated how foundational infrastructure can carry hidden risk. For P7 DarkSword, the iVerify blog remains the authoritative source as the investigation develops.
Disclaimer: This article is for informational purposes only and does not constitute financial or investment advice. Cryptocurrency and digital asset markets carry significant risk. Always do your own research before making decisions.
Read original article on coinlive.me